Related Topics:
Titanhq Network Security Checklist-
Which network security equipment brands are available
Several top brands are leading in network security devices in 2025. Channel Insider lists Palo Alto Networks, Fortinet, and Cisco as the top providers. With networks become even bigger and more complex, Cyber Magazine examines the top 10 biggest network security companies so readers can see what's on offer In today's interconnected digital landscape, network security has become paramount for enterprises of all sizes. The company's platform integrates next-generation firewalls, extended detection and response (XDR), and secure access service edge (SASE) capabilities.
-
Three-layer protection for network security devices
IT security spans three critical layers: Management, Operational, and Technical controls — not just firewalls and antivirus. Businesses with layered security strategies reduce breach costs by an average of 43% compared to single-layer protection (source: IBM Cost of a Data Breach. To address the threats faced by networks and enhance security protection during network design, construction, and operation, the International Telecommunication Union (ITU) defines a layer- and plane-based security framework in the X. 805 security framework, in. How to design, use, and maintain secure networks. Networks are fundamental to the operation, security and resilience of many organisations. It. This involves deploying multiple levels of security controls to protect against all types of cyberattack, eliminate single points of failure in your network security, and minimize the chance of a data breach.
[PDF Version]
-
What are some digital network security devices
The main types of network security devices include firewalls, intrusion protection systems (IPS), unified threat management (UTM) systems, network access control (NAC), email security gateways, web application firewalls (WAF), and VPN gateways. These devices act as barriers between the internal network and potential threats from the outside world. Whether you're a business owner or an IT professional, understanding the. Explore essential security devices in networking with this beginner's guide, covering firewalls, VPNs, IDS, IPS, and more. Firewall appliances and intrusion detection systems are critical components of network security. Top network. Network security solutions are specialized hardware devices designed to protect networks from cyber threats, and modern innovations like Juniper Mist networking for secure, scalable infrastructure further enhance visibility, automation, and overall network performance.
[PDF Version]
-
Network security devices offline
Security cameras can go offline for various reasons, including weak Wi-Fi signals and outdated firmware. Ensuring they have updated. Periodically download the latest Defender security intelligence updates from the Microsoft website. Use a local network share or removable media to distribute these updates to the offline devices. Create Update Scripts: Write PowerShell scripts to automate the installation of updates on offline. I have two FTDs that have been offline for more than a year, and now I can deploy the configuration to change the IP address of the WAN interface to connect to the internet. I now have internet on site, but from a different ISP. We kept working at it and found an interesting solution. d:443 read: connection reset by peer [for support diagnosis: requestID: 7e761b68-a878-915e-af11-2b561484e0e9] "Connection reset by peer"? Not sure where to go.
[PDF Version]
-
Supplier s network security equipment 200G
Powered by a rich set of AI/ML security capabilities that extend into an integrated Fortinet Security Fabric platform, the FortiGate 200G series delivers secure networking that is broad, deep, and automated at any scale. The FortiGate 200G series next-generation firewall (NGFW) combines artificial intelligence (AI)-powered security and machine learning (ML) to deliver threat protection at any scale. Get deeper visibility into your network and see applications, users, and devices before they become threats Powered. Extend the protection capabilities of your Fortinet FortiGate 200G Firewall with comprehensive security services from the AI-powered Fortinet Security Fabric. You can license security services and support à la carte. With a firewall throughput of 3 Gbps and VPN throughput of 6 Gbps, it efficiently handles large volumes of.
[PDF Version]
-
FTTR uses an upgraded version of network security equipment
FTTR is an advanced version of fiber optic technology. It comprises the laying of optical fibers to remote nodes to ensure an entire home or even a building gets access to the robust network. Leisure (Karaoke, Bar, Teahouse. Add security detection mechanism 1. Add conductive contact guards for communication among devices, chip modules and. FTTR can eliminate the need for parallel network infrastructure and multiple intermediate distribution frame (IDF) closets and allows you to reclaim space for more revenue generation with a smaller cable footprint. This paper presents a comprehensive analysis of the FTTR system architecture and protocol stack, focusing on three key technical aspects: centralized. FTTR optimally utilizes fiber optic technology to achieve a robust home optical network. The method is applied to the main gateway equipment and comprises the following steps: acquiring upgrade version information of at least one slave gateway device, and acquiring.
[PDF Version]
-
How many compartments in the network rack are 1U
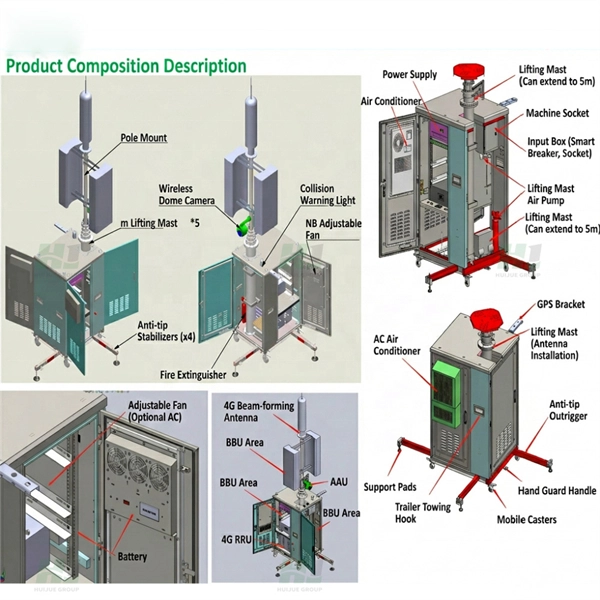
Usually, equipment like servers, routers, and switches is designed in multiples of rack units—for example, 1U, 2U, or 4U—each denoting the amount of vertical space that they occupy in a rack. To illustrate, a 2U device will occupy the same space as two 1U . U (rack unit, RU) is a unit of equipment height in a 19" rack. Important: U describes height only, but a server's real "capabilities" are also determined by chassis depth, internal layout, airflow, rails, power, and expansion (PCIe/risers, NVMe. For example, a typical full-size rack cage is 42U high, while equipment is typically 1U, 2U, 3U, or 4U high. The rack unit size is based on a standard rack specification as defined in EIA -310. This article explains definition, planning, installation tips, and trends. 75 inches, making it compact and suitable for dense setups. A 4U device uses 7 inches, usually designed for high-performance systems requiring extra internal. We explain what 1U, 2U, 18U, 42U, and other configurations mean, discussing precise dimensions, tolerances, and essential parameters. When you step into a modern data center, you're.
[PDF Version]